Explore
Custom software · Backend & API development

Build the backend your business rules require

For teams whose app depends on consistent records, customer permissions and integrations that fail in a predictable way. We build or extend the backend around those rules: clear module boundaries, typed API contracts and tests for the failure paths that matter. The data model, service boundaries and where each rule lives are the decisions that cost years to undo, so we make them on purpose and write down why. Your team receives the code and operating instructions with each increment.

  • 130+People, remote across Poland
  • 44 daysFirst line of code to live, one consumer product
  • 5.0Clutch rating, 11 reviews

This is for you if you need clear rules behind the interface

  • Every feature costs more than the last

    The backend was built by whoever was available. Rules are scattered across screens and services, the same operation gives different results, and changing one place breaks another. New engineers need months to learn where things live.

  • An integration fails halfway through

    An external system times out or returns incomplete data. You need an agreed outcome for the operation and a way to investigate it.

  • Different customers need different access

    The backend must enforce who can read or change each record, whatever screen or API client sends the request.

  • More users expose problems

    Concurrent requests and repeated jobs behave differently from a single-user test. Before usage grows we check each critical path: indexes that match the filters, no N+1 queries, short transactions, jobs that are safe to run twice and connection pools budgeted across replicas.

What you get. A backend your team can reason about

A data model and API contracts

Who owns each record, which operations are allowed and how other systems call them, defined in OpenAPI or a shared schema with generated types. Existing clients, versioning and compatibility are part of the plan.

Module boundaries you can enforce

Each business area gets its own module with a public interface, built as ports and adapters: the rule lives in a use case, the database and external APIs sit behind adapters, and import checks keep other modules out. Your engineers, and their coding agents, can change one area without reading the whole repository.

Working operations that survive failures

Idempotency keys for requests that get retried, an outbox where a database write and a message must both happen, and an agreed outcome for every external call that times out. Tests cover the permissions, invalid inputs and failure paths agreed in scope.

Decisions written down

Architecture decision records next to the code: what we chose, what we rejected and what would justify a second look. Microservices, CQRS or event-driven messaging only where the problem calls for them, with the reason on file for the next maintainer.

Code your team can operate

The implementation, API documentation and tests, plus setup and deployment instructions. Handover covers the decisions a maintainer needs before changing the behavior.

Tech stack. Backend tools your team can maintain

Java with Spring Boot, Node.js with NestJS or Fastify, Python with FastAPI or Django, Go, .NET and Laravel, on PostgreSQL, MySQL or Azure SQL. We build on AWS and Azure managed services where they fit, and choose around the business rules, existing integrations and the people who will maintain the services.

Tech stack

  • Java
  • Spring Boot
  • Node.js
  • NestJS
  • TypeScript
  • Python
  • FastAPI
  • Django
  • Go
  • .NET
  • Fastify
  • Laravel
  • PostgreSQL
  • MySQL
  • Redis
  • Kafka
  • RabbitMQ
  • OpenAPI
  • GraphQL
  • tRPC
  • Prisma
  • Kysely
  • Supabase
  • AWS Lambda
  • Amazon ECS
  • Amazon RDS
  • DynamoDB
  • Amazon SQS & SNS
  • API Gateway
  • Azure Functions
  • Azure App Service
  • Azure Service Bus
  • Azure Cosmos DB
  • Azure SQL

How we work

Define the rules before the endpoints

Some backend decisions are cheap to change later. The data model, module boundaries and how services talk to each other are not, so we make those with the people who understand the operations and record the reasons. The scope names the first complete operation your team will be able to use and the dependencies that affect its date. You get a written status daily at first, then weekly once trust is there.

You want to build it stable enough so you can remove any piece without everything else falling apart. It’s way harder than it sounds.
Jarosław CzyczBusiness Analyst and FinTech Expert, Pirxey
  1. Map the business operations

    Start with the user action, the data it changes and the external systems it touches. We group the rules into domain boundaries (bounded contexts, if your team speaks DDD) and mark the decisions that would be expensive to reverse. You get an agreed first slice and the open questions before we estimate.

  2. Agree the model, contracts and estimate

    We write the data model and API contracts with the teams that will consume them and record each architecture decision with its trade-offs. Direct calls or events, one service or several: the choice follows the problem, not the trend. You receive an estimate per module and a date for the first usable increment.

  3. Build a complete operation

    One vertical slice: the API adapter, the use case with its rule and the ports to storage and integrations. Tests cover the domain rule, the contract, the database mapping and the agreed failure paths, like a retried request or a timeout after the write. You get a deployable increment with code, tests and documentation for review.

  4. Release and hand over the operating work

    We plan the rollout and how to roll it back, add trace IDs and alerts for the failures that matter, and document how to inspect them. Your team takes over, or we agree continued work.

Proof, not promises

Featured
Security · Government
Matic · Poland

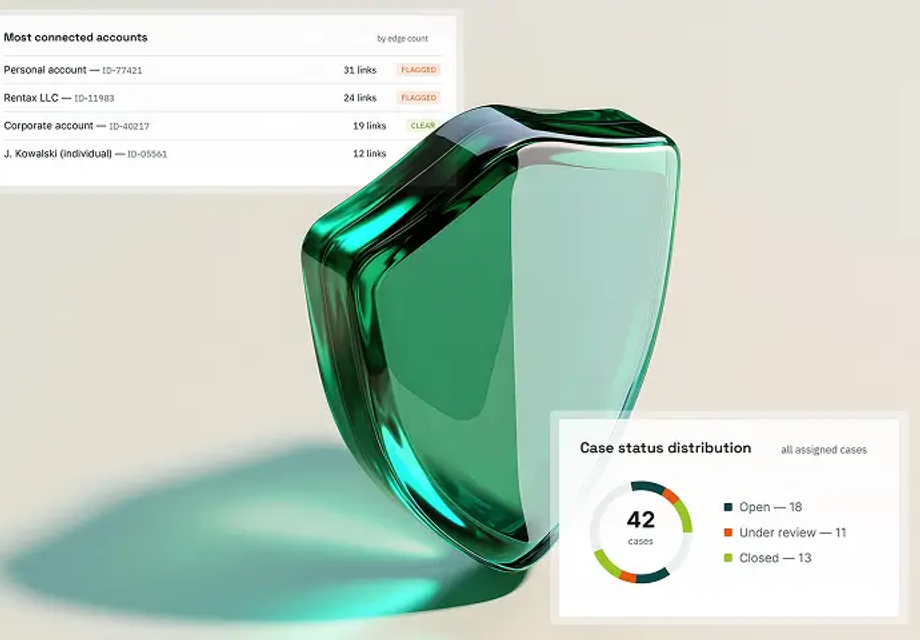
Financial-crime investigation software for Poland's authorities

1.5M+ records normalized in one case
Read
FinTech · Government
NDA · USA

AML-grade oversight for U.S. political ad spend, built from scratch

5 mo zero to shipped MVP
Read

Questions about server-side delivery

  • No. We work in your repository, your cloud and the tools your team already uses. If one of them gets in the way of the work, we tell you what and why, and you decide.
  • With a 30-minute scoping call. We look at what you have and what you need, then propose a first step with its scope and price before any work starts.
  • Bring a business operation, the systems it touches and any existing API documentation. Tell us who owns the frontend and which date matters. The first call establishes what needs discovery before we estimate the build.
  • We estimate the agreed scope after discovery, with costs per module so you can choose what to build first. A defined scope can be quoted; an evolving product can use a dedicated squad with an agreed budget. We confirm the billing model before starting.
  • We name the first complete operation and its delivery date in the plan. The estimate depends on the data model, integration access and compatibility requirements. You receive deployable increments with tests and documentation as the work progresses.
  • Yes. We review its contracts and current consumers before proposing changes. Compatibility and rollout requirements become part of the plan, so the team can see which interfaces stay and which need to change.
  • Only when the problem justifies them. Most backends we start are a modular monolith: one deployable application with strict module boundaries, so a module can become its own service when traffic, team size or release schedule demands it. CQRS and event-driven messaging get the same test. We write down the reason for any new service boundary before taking on the deployment and coordination work it brings.
  • Little on day one. The bill comes later: features that take weeks because every change touches five places, outages from retries that charge twice or jobs that run twice, and new engineers who need months to find where the rules live. Maintenance is where a wrong shape gets paid for. Even our own product, PirxeyOS, built in about 20 working days, needed 51 data-consistency fixes and 26 API and integration fixes after go-live. If you already have such a backend, we start with a diagnosis and tell you what to keep and what to rebuild.
  • We define what should happen when a dependency fails, times out or returns incomplete information. The implementation and tests cover those agreed cases, with operating notes for investigating work that a failure left unfinished.
  • You keep the code, API contracts, tests and setup instructions. We plan a handover to your team or agree continued work. Monitoring and support responsibilities are set before launch.
  • Financial Trail, investigation software we build with Matic: in one case, more than 1.5 million transaction records from 350 raw files across 35 bank accounts, normalized into one schema. Matic's spec targets tagging matches across 1M+ records in under 30 seconds. A US campaign-finance platform on NestJS with Lithic and Plaid: an MVP in about five months. A New York construction platform whose backend we rebuilt from scratch on NestJS and PostgreSQL: five core modules for three user roles.

How we think about this, in our own words

Interactive briefs and articles by our team, picked for this service

Architecture is what the agent sees

How module boundaries, typed contracts and tests keep an agent's changes inside one part of your backend, with a Java/Spring example.

Read the brief

PirxeyOS: 20 days to build, 30 weeks to keep alive

What our own backend needed after go-live: 51 data-consistency fixes and 26 on APIs and integrations, from a 587-commit log.

Read the brief

The Most Expensive Decisions in IT Are the Ones Nobody Officially Makes

Why data model and integration choices left open for months cost more than the ones made on purpose.

Read the article

Describe the rules your backend must enforce

Additional details (optional)

We reply within one business day.

Pirxey will process your data to answer your inquiry. Details in our Privacy Policy.